
Security and trust
Built for the examiner.Proven by the auditor.
Callvu runs regulated processes for banks, insurers, carriers, utilities and hospitals. Here is how we protect the data inside them, and how we prove it.
 SOC 2 Type IIClean audit report
 PCI DSSAttestation of Compliance
 HIPAAPHI safeguards
 GDPRMinimization and erasure
 CCPAConsumer privacy
- Each customer's data in its own database
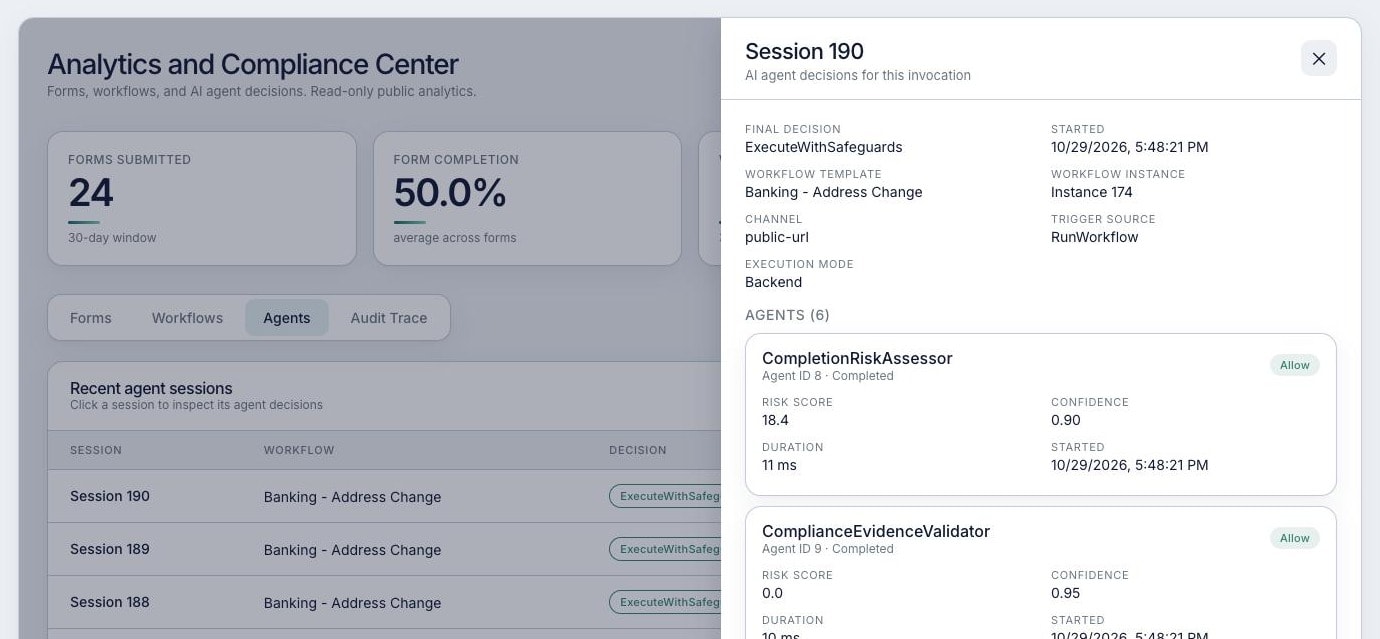
- Immutable audit logs, kept 14 months or more
- Independent penetration test every year
- AI off until you turn it on
Certifications
Independently audited.Not self-declared.
Audited
SOC 2 Type II
Security and Confidentiality. Audited by Ernst & Young, with a clean opinion on the design and operating effectiveness of our controls.
Attested
PCI DSS
Attestation of Compliance for payment card data protection.
Active
HIPAA
PHI safeguards, access controls and audit logging, with PHI masking live and tested.
Active
GDPR
Data minimization, purpose limitation and the right to erasure.
Active
CCPA
Consumer privacy rights for California residents: access, deletion and opt-out.
Data protection
Isolated by design.Encrypted everywhere.
Identity and access
The right people.Only the right people.
Single sign-on
Enterprise SSO through Okta over OIDC, with multi-factor authentication enforced at your identity provider.
Roles that fit your org
Administrators, designers, operators and viewers, with permissions per module and segregation of duties.
Least privilege, inside Callvu too
Production access only over VPN with SAML and two-factor authentication, reviewed periodically and revoked on the last day.
AI governance
AI on your terms.Off by default.
Off until you turn it on
AI features are enabled per tenant, by you. Nothing goes to an AI service unless you switch it on, and one setting turns it all off.
Never used for training
What your customers submit is not used to train models, and model providers keep no prompts or outputs.
Masked before it is sent
Configurable anonymization masks the fields you choose before any AI processing. Analytics send cumulative data only.
Inside our cloud
AI runs on managed models within our own cloud environment. If AI fails, the process keeps running.
1. What the customer enters
- Full nameDana Lee
- Date of birth04/12/1986
- New address18 Elm St, Austin TX
2. Masked by your policy
- Full nameD••• L••
- Date of birth••/••/••••
- New address18 Elm St, Austin TX
You choose which fields are masked, per data type.
3. AI, inside our cloud
- Managed models in Callvu's own cloud
- Never used for training
- No prompts or outputs kept by the provider
- If AI fails, the process keeps running
AI is off until you turn it on, per tenant. One setting switches it all off again.
Operations
Watched, tested,and ready to recover.
Data governance
Your data stays yours.From first field to last day.
Audit evidence you can keep
Run records, documents, state transitions and audit logs are kept for at least 14 months. Audit logs are immutable.
Collect only what you need
You define every field a process collects, and which ones are required. Nothing is captured speculatively.
Yours when you leave
At the end of a contract, your database is handed back to you or securely deleted. Your choice.
For your vendor assessment
The Architecture and Security Document.
Eighteen sections covering infrastructure, tenant isolation, data flows, encryption, access, compliance, retention, vulnerability management, recovery, AI governance, the development lifecycle and incident response. Shared on request.
Bring your security questionnaire.
Our team will answer it, and walk your security reviewers through the controls.